Custom roles, role bindings and groups are Enterprise features. The built-in organization and
team roles work on every plan. Creating custom roles, listing role bindings and creating groups
need an Enterprise plan, and a self-hosted deployment needs an Enterprise license. The Roles
API refuses calls without one with HTTP 402 and the error code
enterprise_plan_required. To enable it, contact
enterprise@langwatch.ai.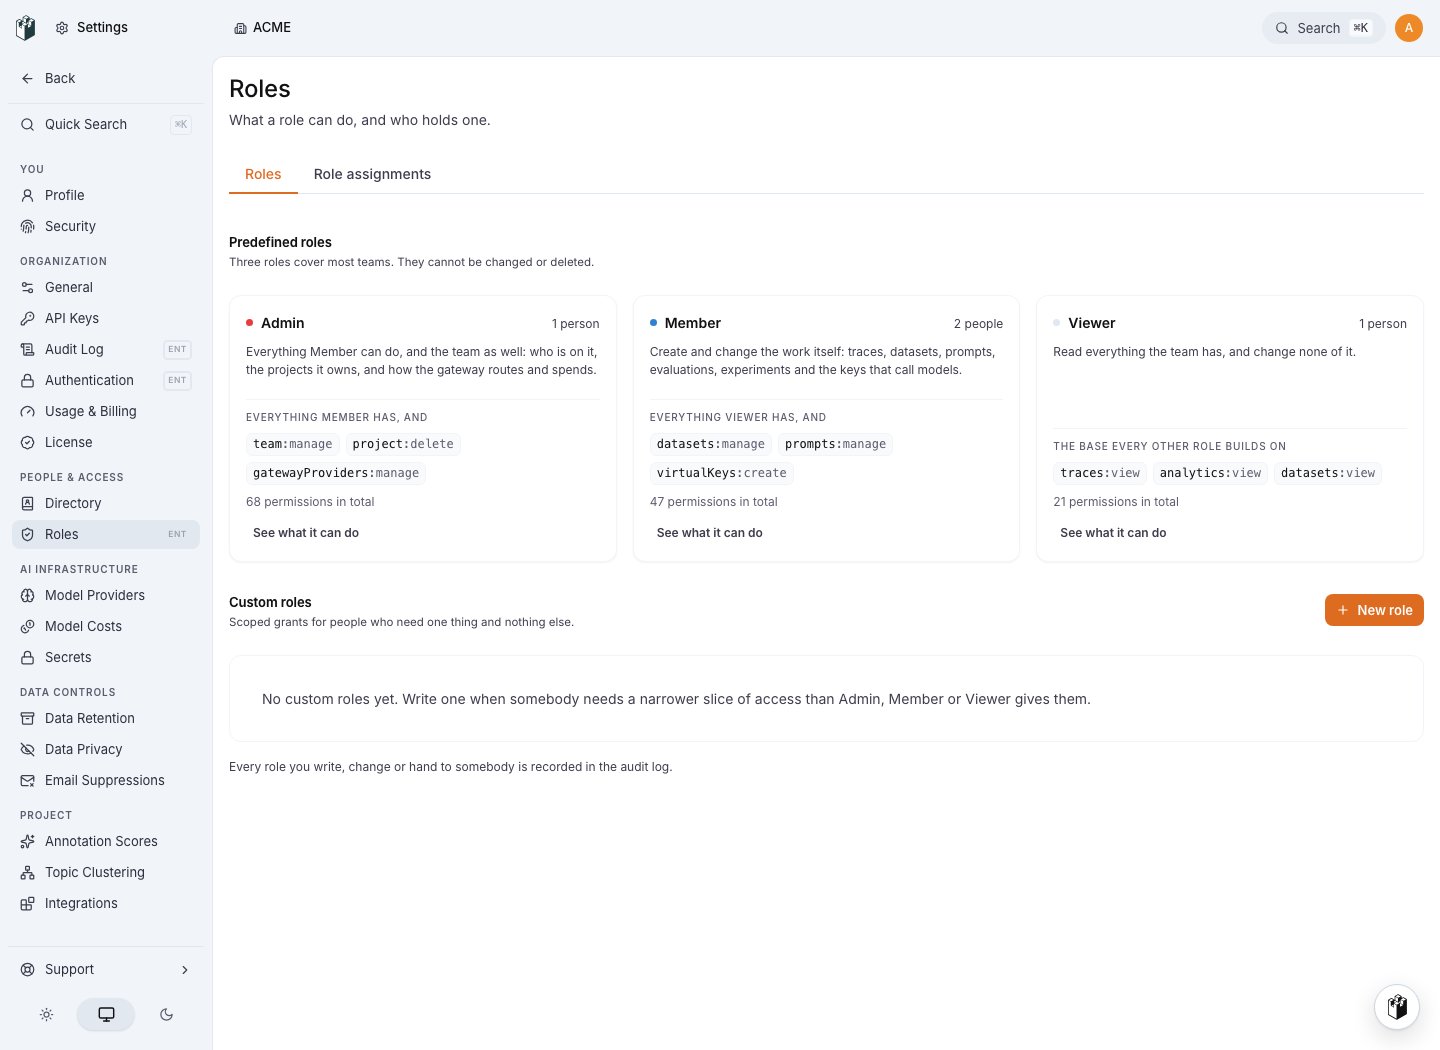
How access is structured
A permission is aresource:action pair, for example traces:view or datasets:manage. A role is a named set of permissions. A role binding gives a role to a person, a group or an API key at one scope: the organization, a team or a project.
LangWatch has three scopes:
Every member of the organization has an organization role. A role binding at the organization scope applies to every team and project in it, which is how an organization Admin reaches everything. Below that, access to a team or a project comes from a binding on that team or that project.
Organization roles
Set the organization role per member in Settings > Directory > People. The role decides what a person can do at the organization level and how their seat is counted.
A Lite Member uses a Lite seat, which is counted separately from full seats. In the settings pages a Lite Member can only be given the Viewer role on a team or a project. A group binding above Viewer applies as Viewer for a Lite Member.
A Developer uses a Developer seat, which is counted but never limited. A Developer cannot be given a binding on a shared team, a shared project or the organization; the request is refused naming the seat. Moving a member onto the seat deletes those bindings. The API accepts
DEVELOPER wherever it accepts an organization role.
Also check: Members and Teams for seats, invites and how to change a member’s role.
Team roles
A team role applies to one team and, through inheritance, to every project in it. A binding on a single project adds access on that project only, and never removes what the team role already grants. The built-in roles are Admin, Member and Viewer.
A Viewer reads. A Member creates and edits project work, sees costs, and manages its own virtual keys. An Admin also manages the team, deletes projects, and manages the AI Gateway configuration.
Actions
share and viewOtherPersonal are never implied by manage. Grant them explicitly.
Resources
Each table lists the actions a resource accepts. Resources marked organization only can only be granted by an organization-scoped binding; a team or project binding never grants them, even through a custom role that lists them.Core
Product
Platform
LangWatch AI Gateway
AI Governance
Custom roles
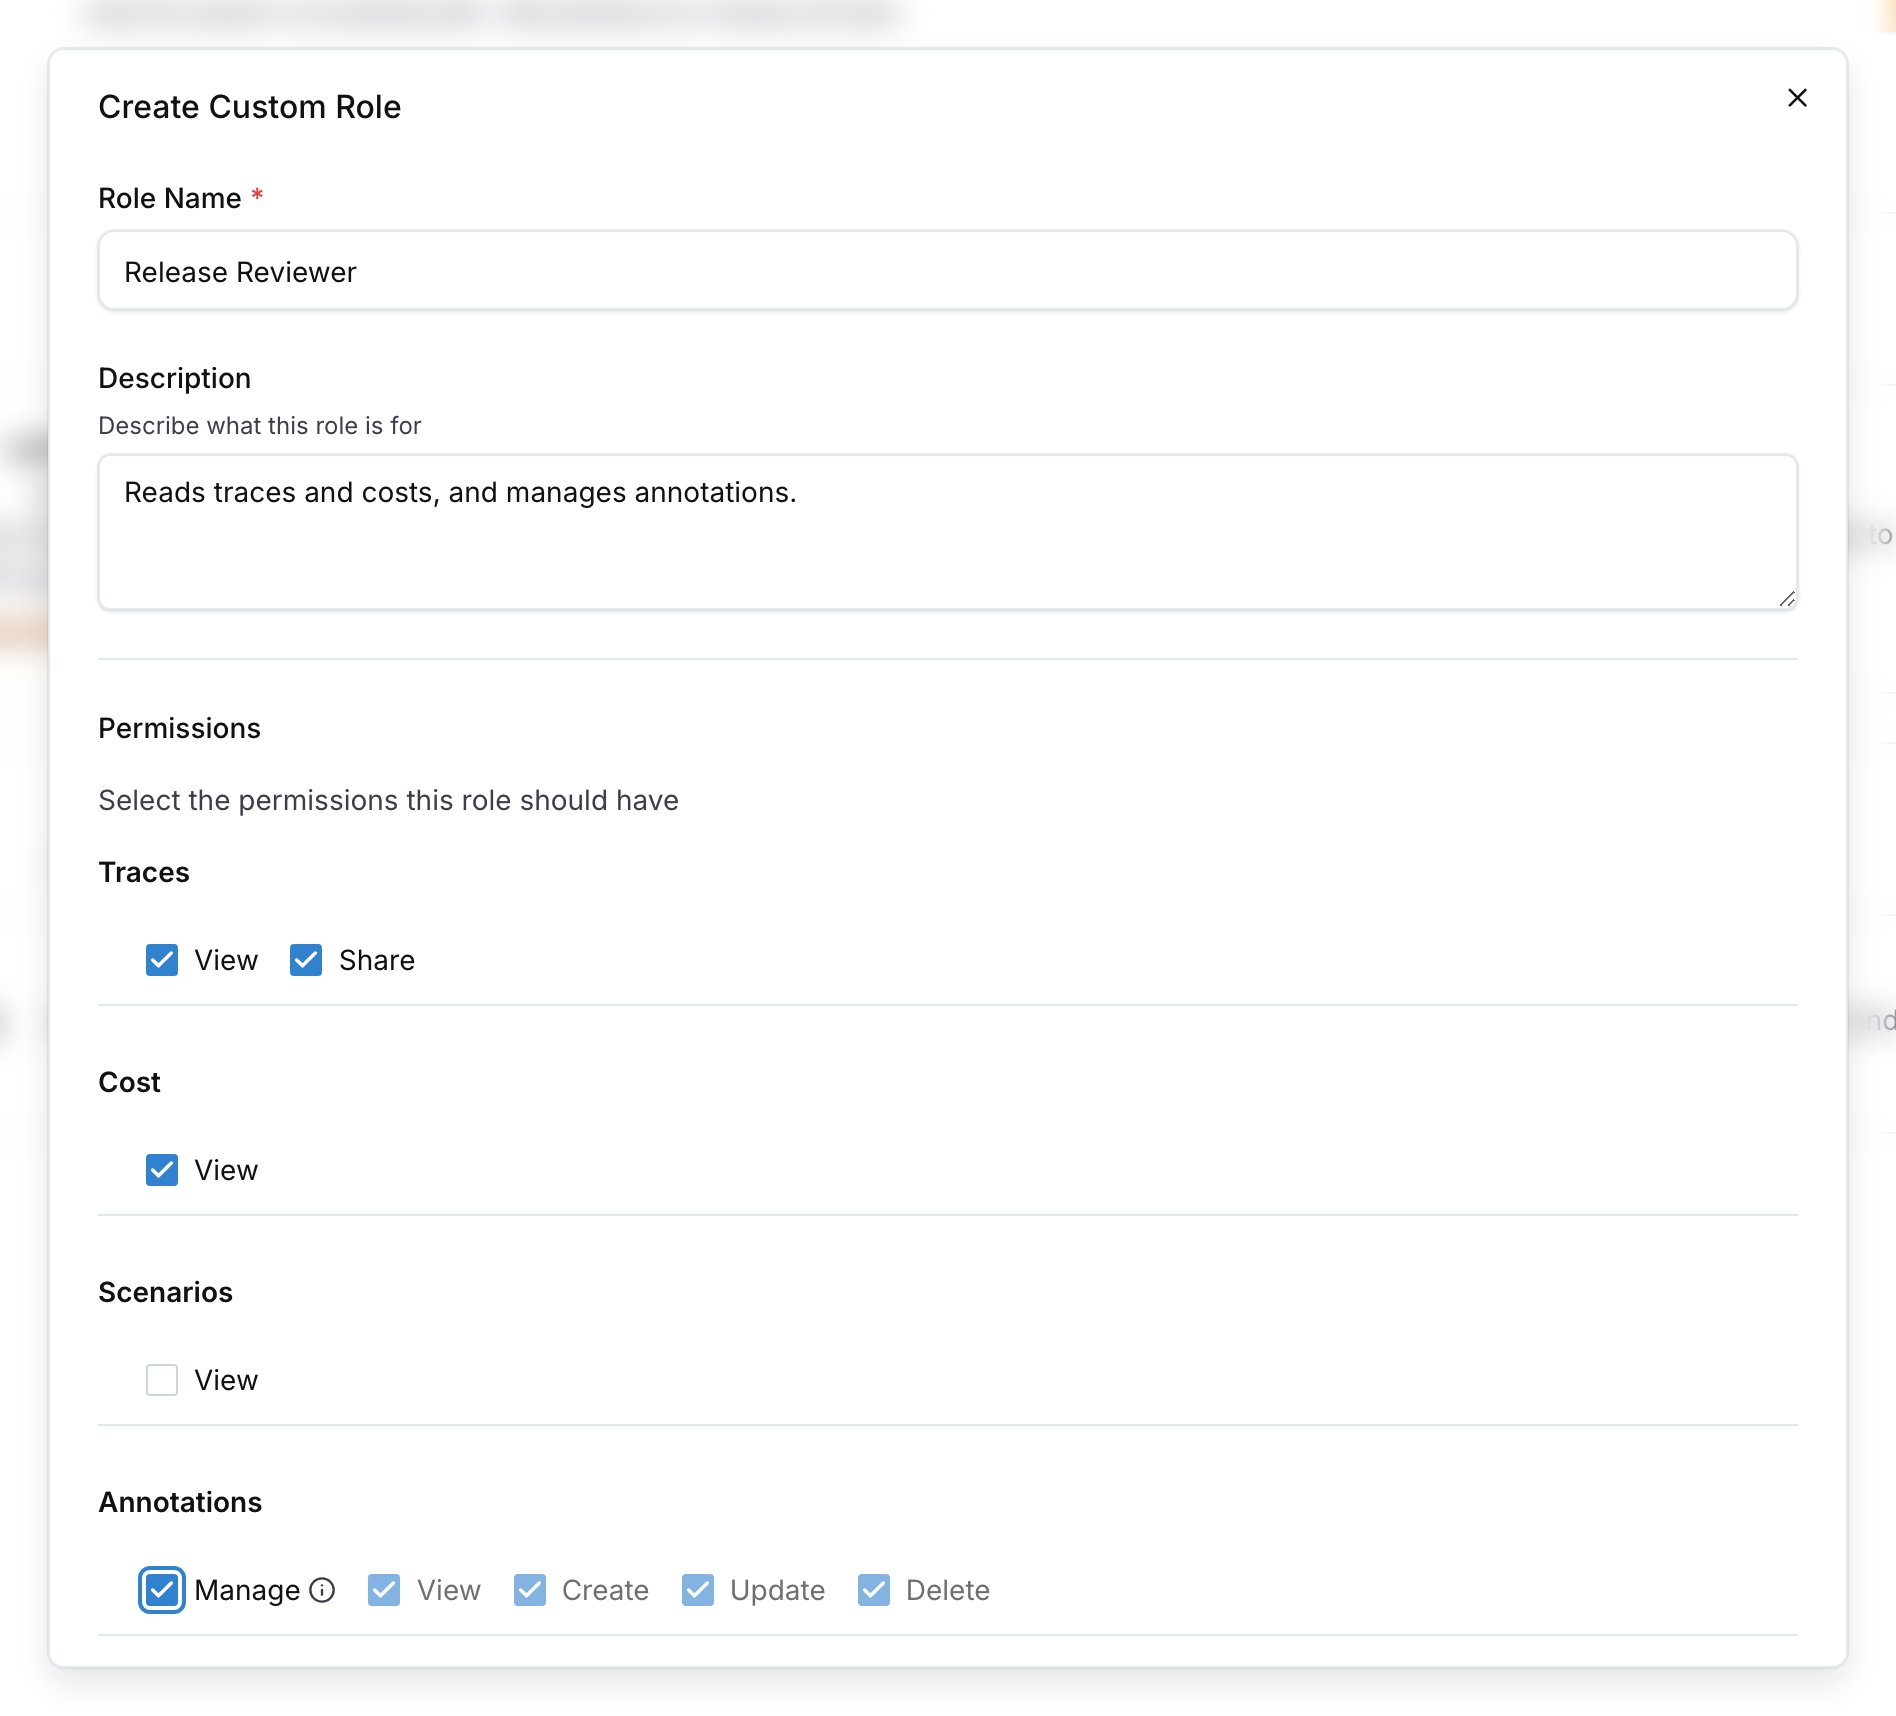
A custom role is a named permission set you define. Create it at Settings > Roles & Permissions withorganization:manage. Custom roles are Enterprise.
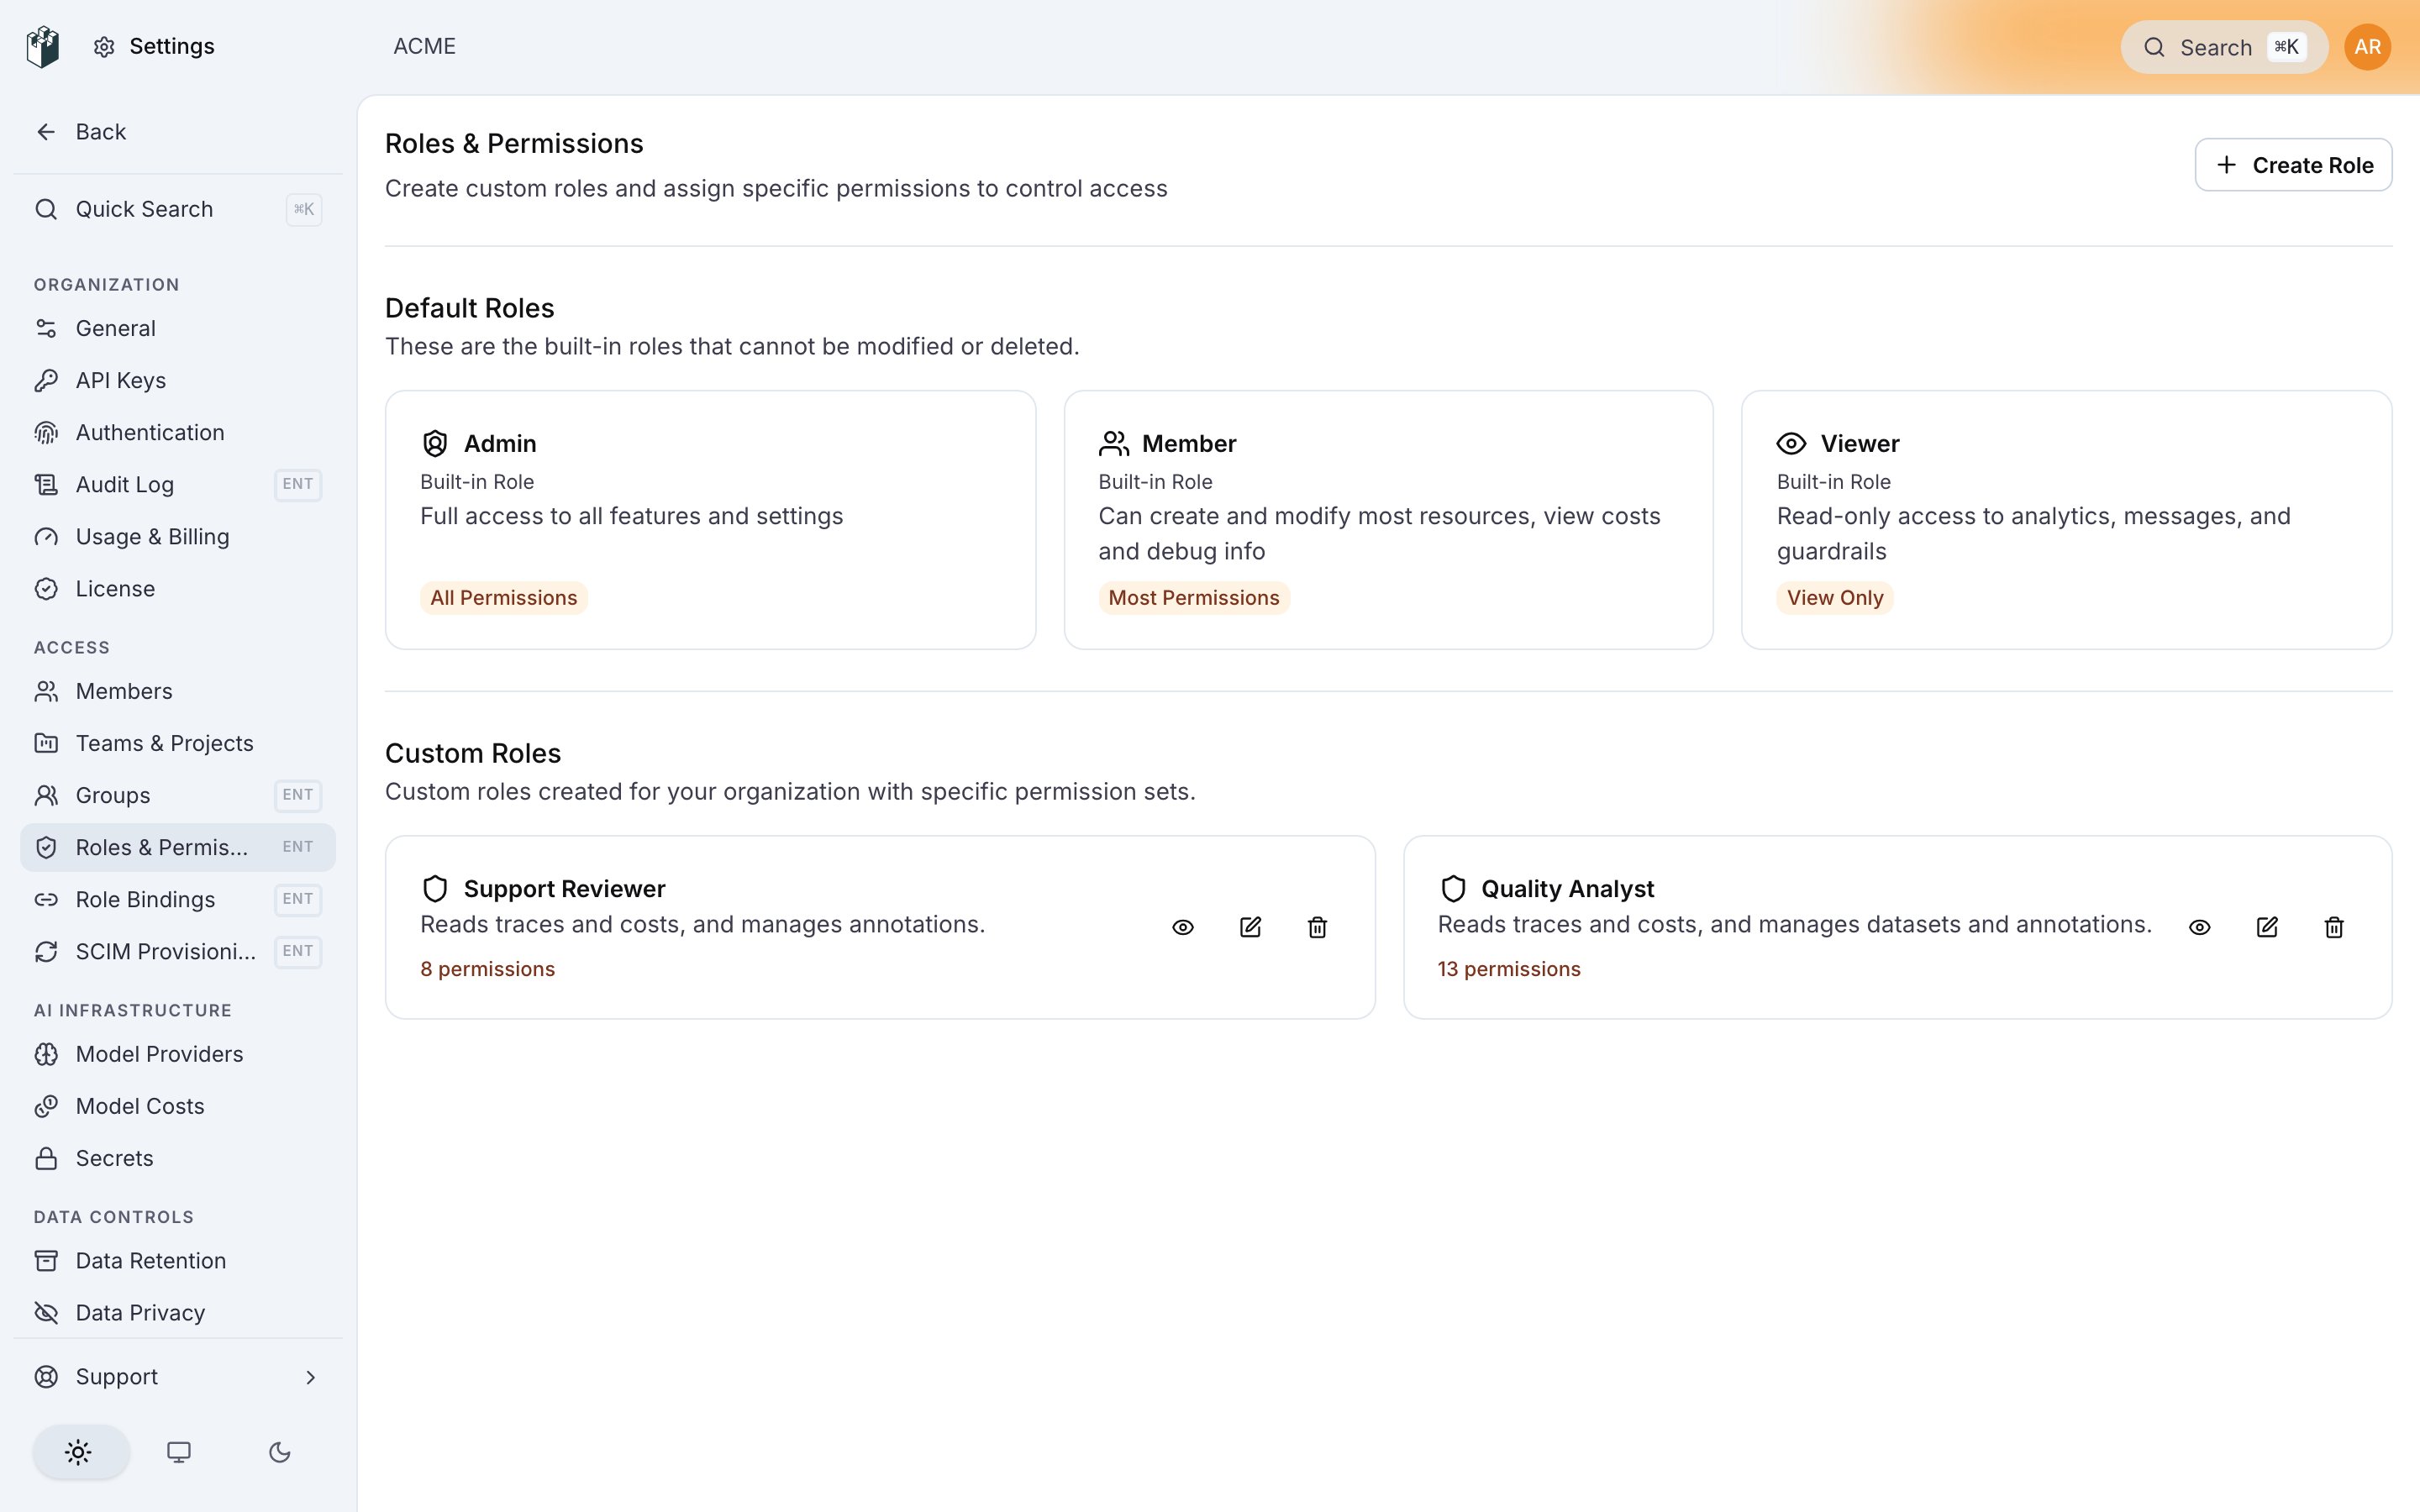
Expand a permission category and choose None, Read or Full access
for each resource. Some resources only support Read. The preview explains what
the role permits at the selected scope. Select Create role to save it.
Role assignments
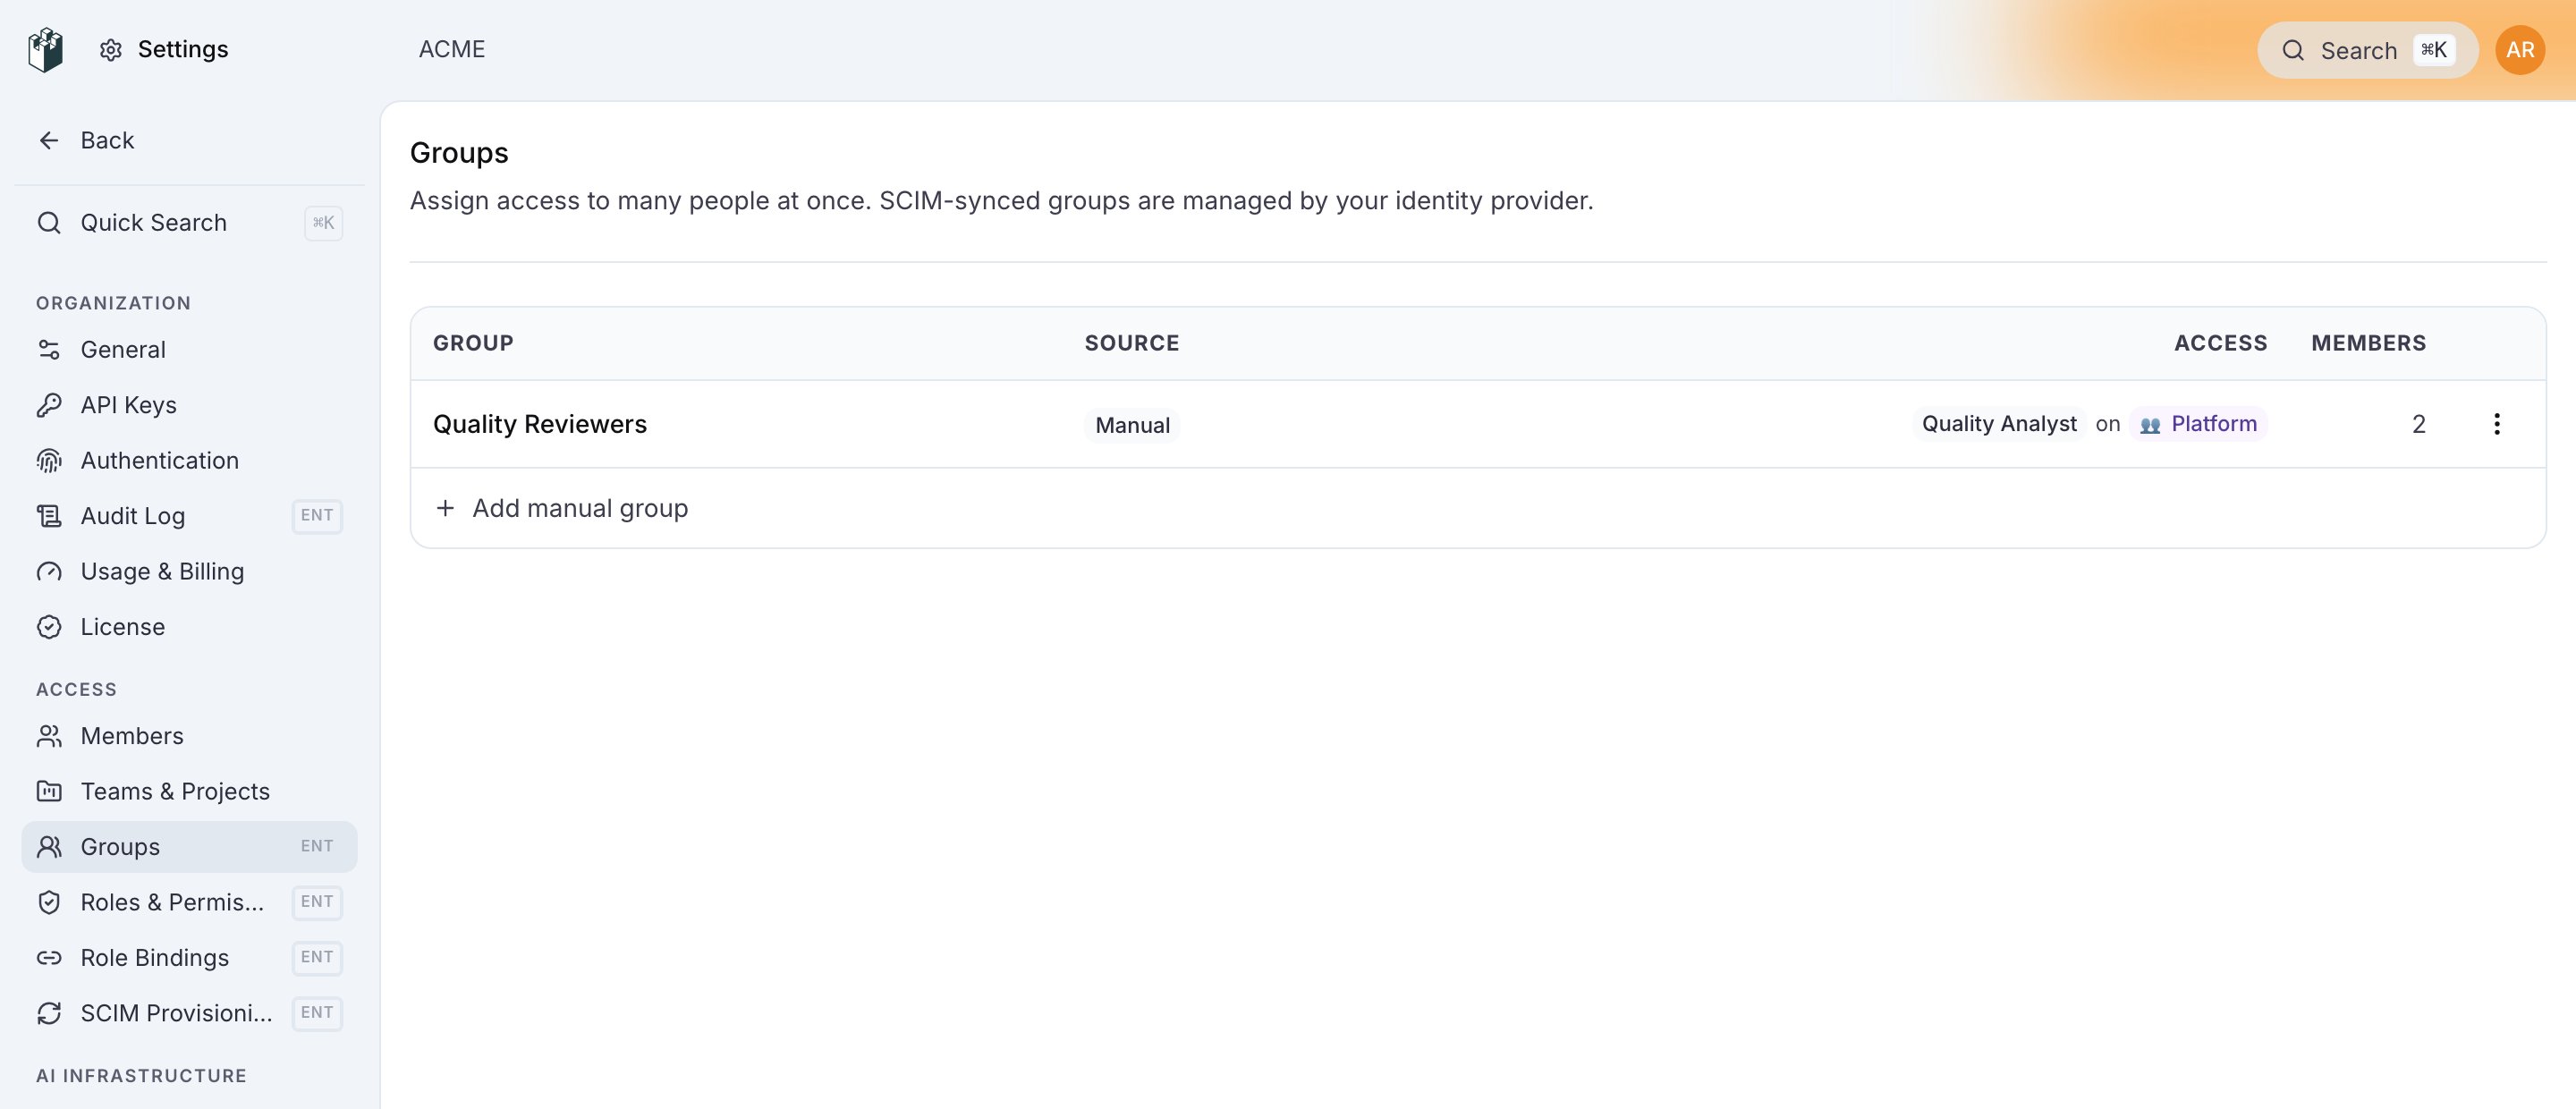
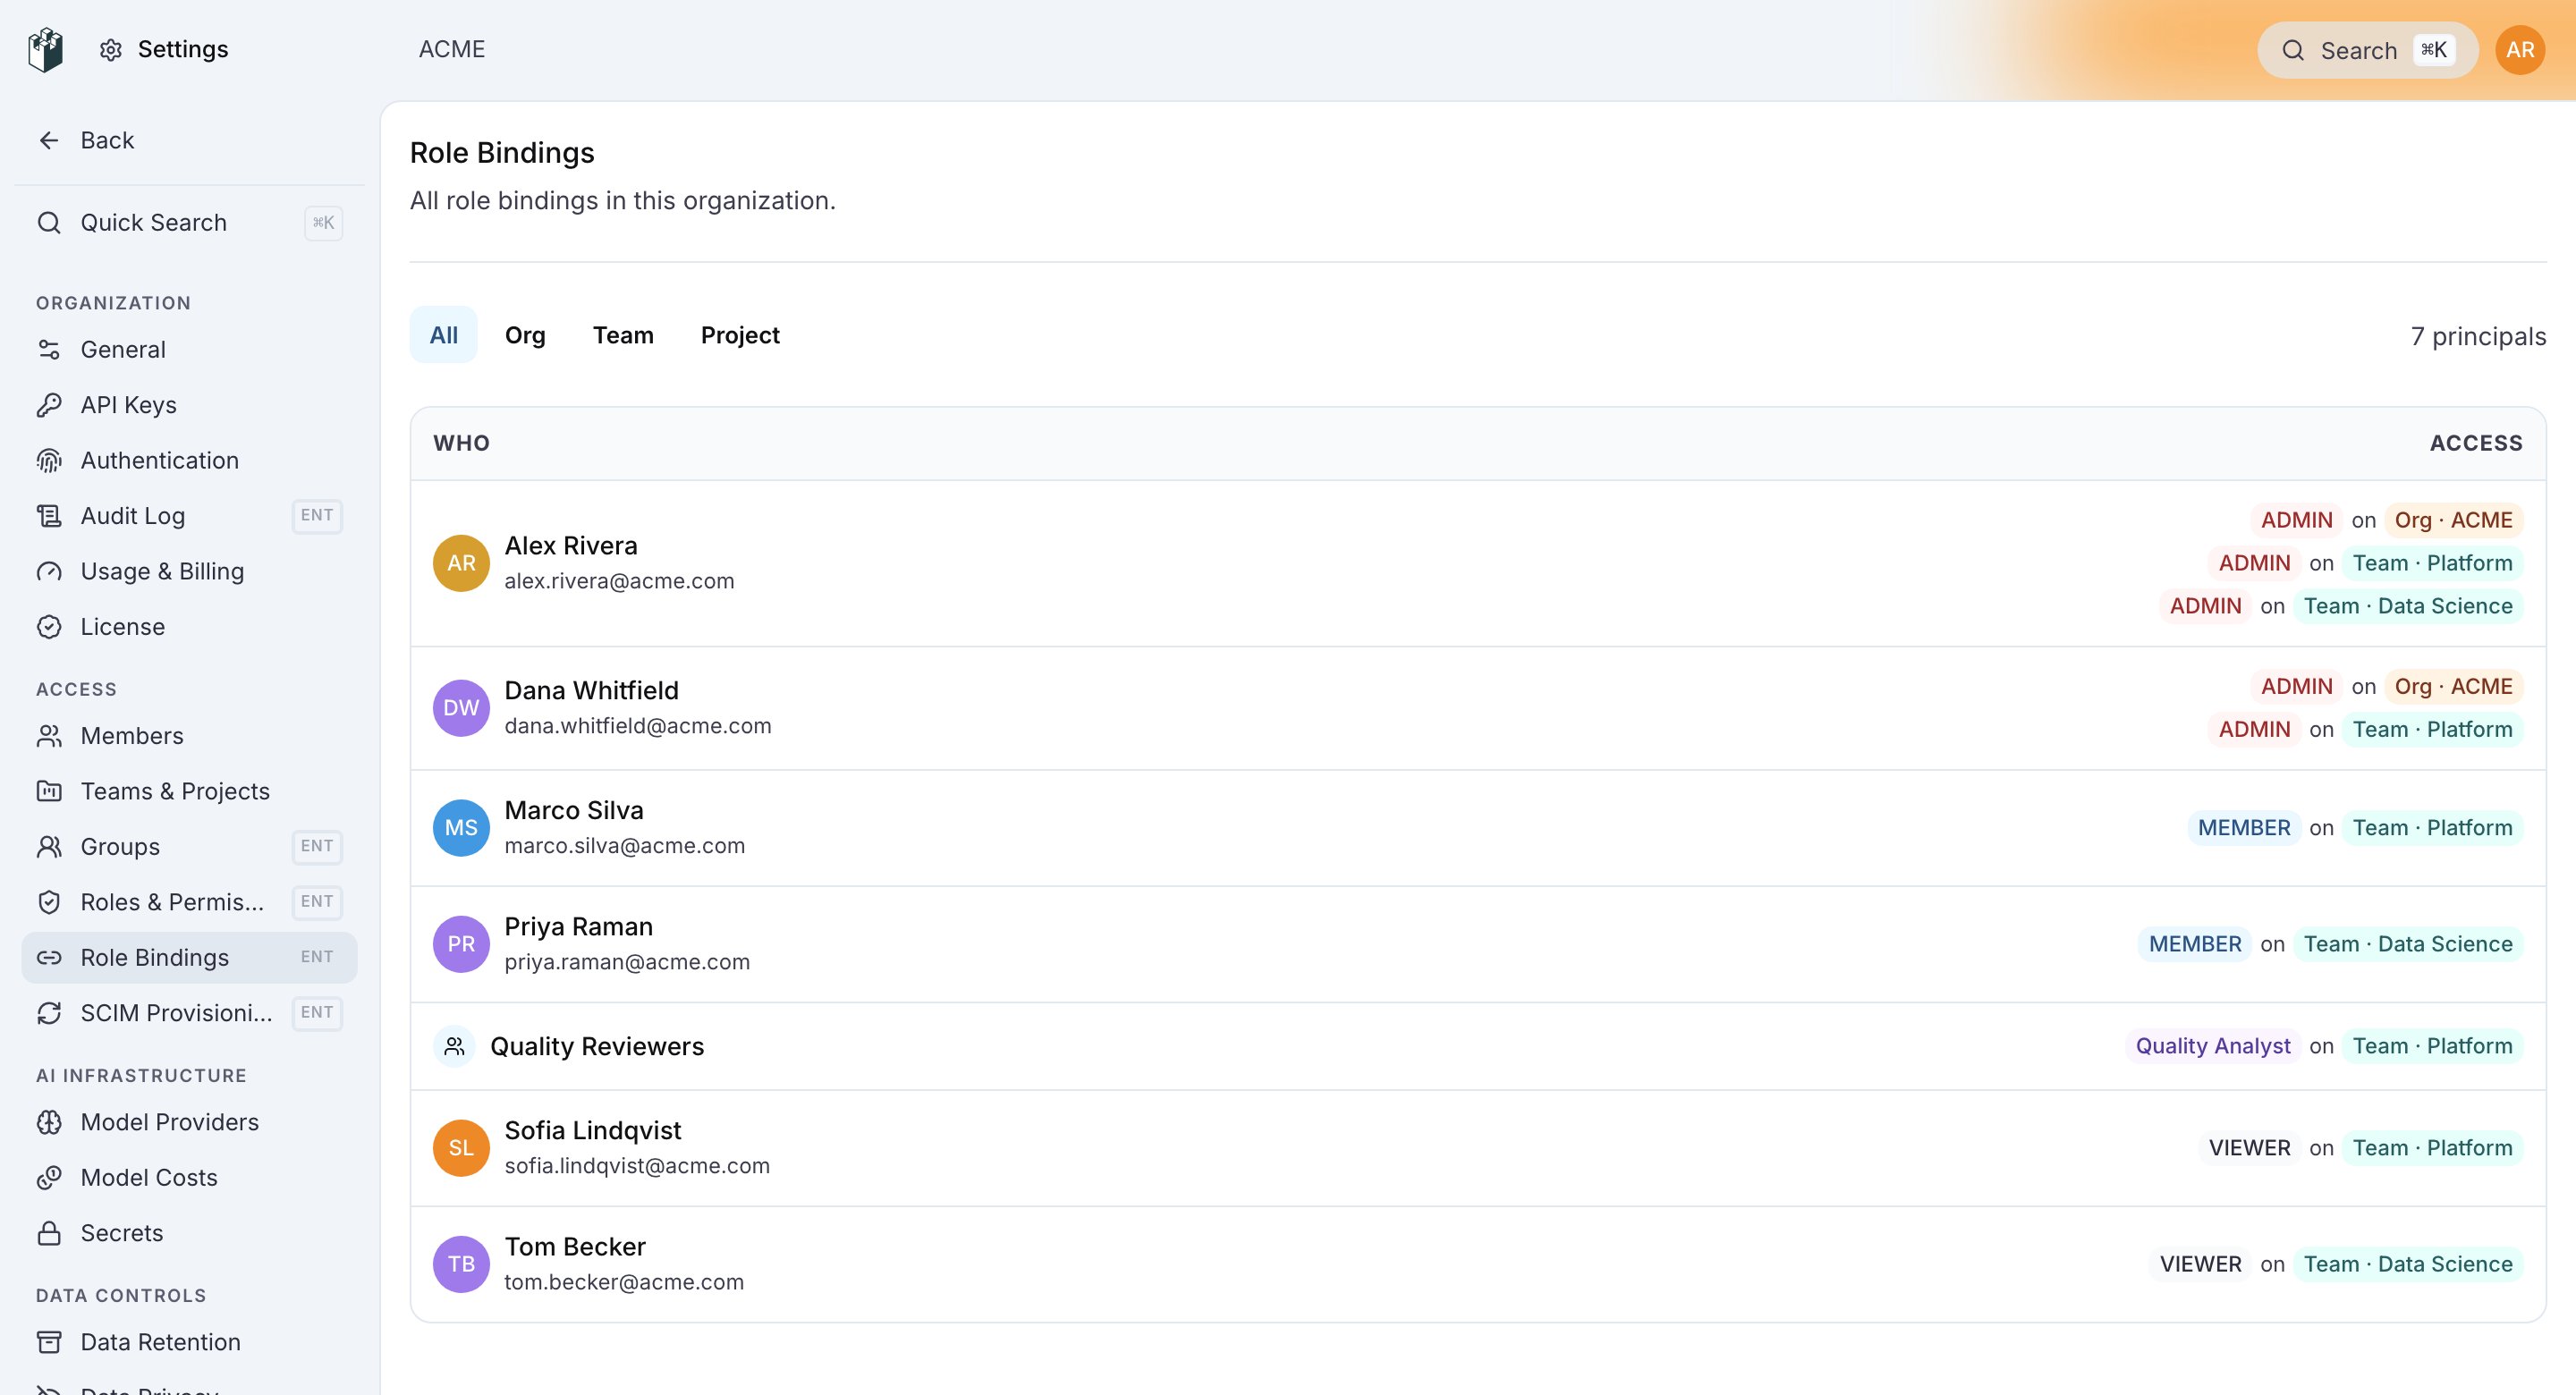
The API calls this a grant (formerly a role binding). In the product, a role assignment is one row: who, which role and which scope. See Roles & access.
You create role assignments for users from Settings > Directory > People and
Settings > Directory > Teams & projects, and for groups from Settings > Directory > Groups. Open
Roles, then choose Role assignments to list every assignment in the
organization. Filter it by organization, team or project scope. This tab is
read only.
Groups
A group gives the same assignments to many people at once. Create a group at Settings > Directory > Groups (Enterprise), add members, and assign roles at any scope. An assignment on a group applies to every member of the group, and the People tab shows it as “via” the group. A group synced from your identity provider through SCIM keeps its name and membership under the identity provider’s control: you bind roles to it in LangWatch, and the identity provider decides who is in it.